When we talk about cybersecurity, it’s easy to end up talking about systems, networks, and data. In the care sector, we need to start somewhere else, with people. Because when technology is disrupted, the impact doesn’t stay behind a computer screen. It reaches those delivering care, families and, most importantly, the people who depend on that care and support every day.
I’ve spent more than 30 years in policing, including working in cybercrime, economic crime, and digital forensics. Technology has changed enormously during that time, and criminals have changed with it. What hasn’t changed is their willingness to exploit an opportunity.
People working in care already understand how important their systems and information are. My concern is what criminals see when they look at organisations from the outside, and how we can make it harder for them to take advantage.
Cybercriminals can now operate at enormous scale. They don’t need to know an organisation or understand what it does before looking for a way in. Technology allows them to scan large numbers of internet-connected systems for weaknesses. They can find the open door first and look at the name above it afterwards.
That matters for a sector made up of organisations of all sizes. A smaller provider isn’t automatically hidden because of its size. Sometimes, the opportunity itself is what attracts attention.
But an attack doesn’t always stop with the organisation where it begins. Care providers work with suppliers and partners, so disruption elsewhere can reach the services and people that depend on them.
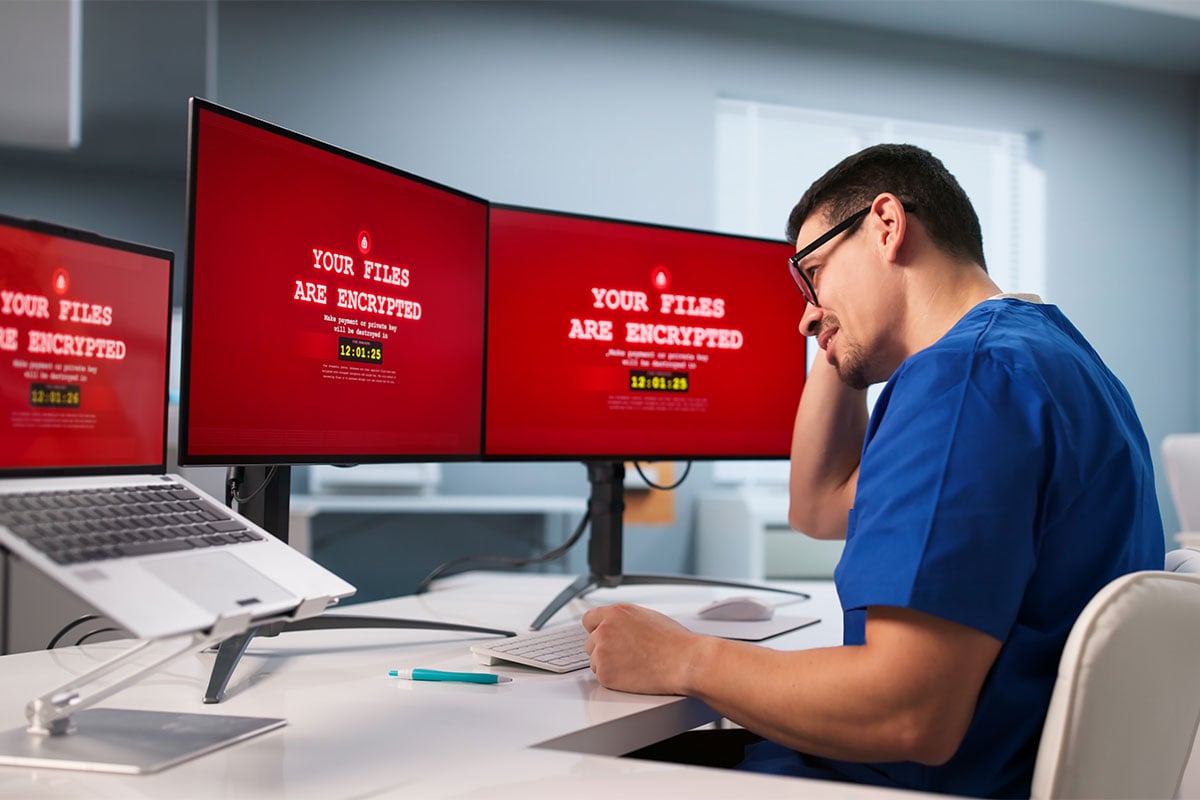
We saw just how serious that can become following the 2024 ransomware attack on pathology provider Synnovis. The attack significantly reduced its ability to process blood tests. Appointments and procedures were postponed, tests rerouted, and NHS staff had to work around the disruption to keep care moving. Some samples eventually had to be discarded because too much time had passed for analysis.
Synnovis was an especially serious incident, but it showed how quickly a cyber attack can move beyond technology. The disruption reached staff, services, and patients, demonstrating how an incident affecting one organisation can have consequences elsewhere.
From a policing perspective, this is why spotting vulnerabilities and suspicious activity early matters. The sooner you know something may be wrong, the more opportunity there is to investigate and act before it becomes a bigger problem.
Police CyberAlarm (PCA) is a free, Home Office-funded policing service available to organisations across the UK. Its Vulnerability Scanning service checks registered websites and external IP addresses for known weaknesses that could be exploited. Organisations can also use the Secure Sensor, which uses firewall data to identify suspicious or potentially malicious activity coming towards their network from the internet.
Police CyberAlarm doesn’t see the content of communications. Instead, it gives organisations information about potential threats and vulnerabilities so they can investigate and act on what they find.
There is another benefit too. What we see happening around one organisation can help us recognise similar activity elsewhere. Criminals often use the same methods against multiple targets, so spotting those patterns can help policing understand where threats are developing and share that knowledge more widely.
For care providers, this isn’t simply about protecting technology. It’s about reducing the risk of disruption to services people rely on. The earlier a potential problem is identified, the more opportunity there is to address it before it affects the delivery of care.
Behind every system are staff trying to do their jobs, families depending on services and people relying on care being there when they need it.
That’s ultimately what we’re trying to protect.
For more caretech news, check out the other articles on the website, and for more information please email us at roshini.bains@starmediaservices.co.uk